Bvostfus Python: A Complete Guide to Installation, Issues, Updates, and Real-World Use
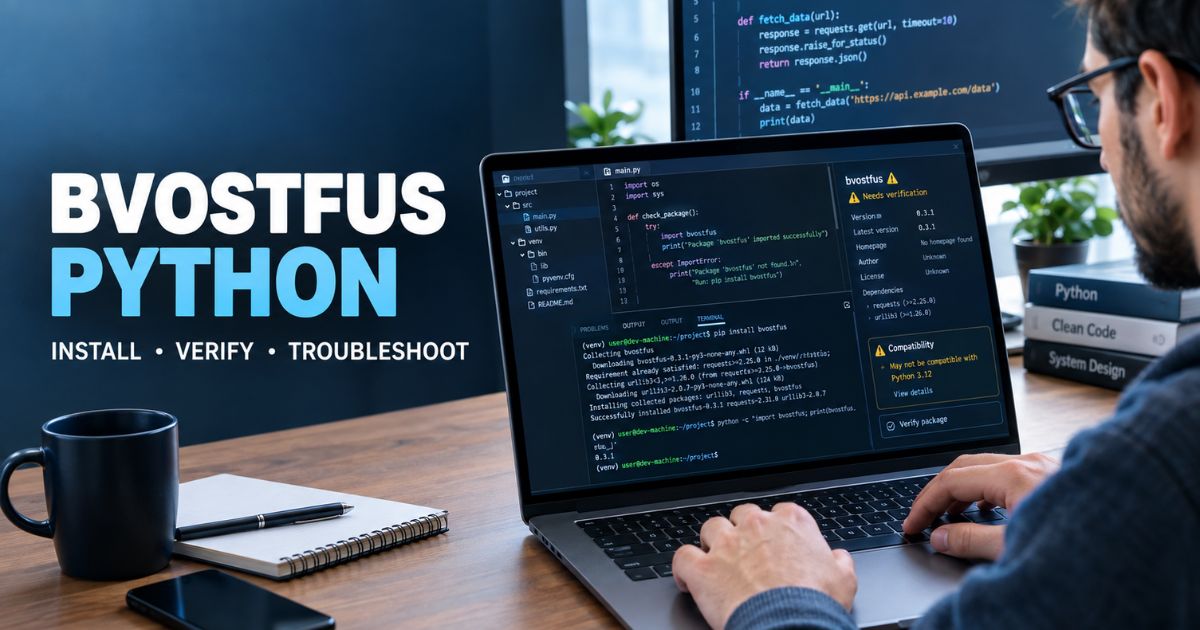
Bvostfus Python isn’t a verified Python package, framework, or tool. As of September 28, 2026, the Python Package Index (PyPI) had no project named bvostfus-python, bvostfus, or bvostfus_python. A GitHub repository search for “bvostfus” returned nothing. Even so, plenty of websites describe it as real software, and a few give install commands for it.
That mismatch is the real story. If you found the name in a tutorial, a requirements file, or an error message, the sections below cover what’s known, what isn’t, and how to check any unfamiliar package before it touches your machine. You’ll also find fixes for the install and import errors you’re most likely to hit, plus established tools that handle the jobs this term is usually said to do.
Quick answer
- Is it real? No verified software by this name has been found.
- Can you install it? No trustworthy method exists. Skip commands from pages that can’t point to a maintainer and a source repository.
- What now? Verify the exact name and source, or choose a documented tool for the job you actually need done.
What Is Bvostfus Python?
Nobody has published a verifiable definition. What exists is a cluster of web pages that use the term and disagree about what it means.
What the Term “Bvostfus Python” Appears to Refer To
Right now, it’s a label rather than a product. It appears in tutorials and guides, but no maintainer, project site, or source code stands behind it. You can find plenty of writing about it. You can’t find anything to download and trace back to a person or organization.
Is Bvostfus Python a Python Package, Framework, or Something Else?
Online descriptions conflict. One page calls it a Python-based framework or environment for development workflows. Another presents it as a beginner-friendly way to learn Python. A Medium post describes an automation package, and a further page walks readers through a command-line tool. Each label implies something checkable. A package would have a registry listing. A framework would come with documentation and source code. A command-line tool would have an installable entry point, and a teaching method would have lessons. None of those has surfaced.
Why the Meaning of Bvostfus Python Is Unclear
Three things muddy the picture. No primary source exists, so every description is secondhand. The pages contradict one another. And some share nearly identical titles and phrasing, which suggests reused content rather than independent research. Some also sit on sites named after the term itself, so they can look like separate confirmations when they may not be.
What Can and Cannot Be Verified About Bvostfus Python
As of September 28, 2026, you can verify these points:
- PyPI has no project under the three spellings tried.
- A GitHub repository search for the term returns no matches.
- Several websites describe it, and their descriptions conflict.
You can’t verify these:
- Who created it, or whether anyone did.
- What it does, if anything.
- Whether any install or update command from those pages works.
- Whether it’s safe or unsafe. No evidence points either way.
Missing evidence isn’t proof of absence, since private indexes and unpublished code exist. But it does mean there’s nothing to trust yet.
Is Bvostfus Python an Official Python Project?
Python has no central approval body for third-party packages, so “official” can mean two things. Part of Python itself means shipped with the interpreter and documented in the standard library reference at docs.python.org. A legitimate third-party project means published through a registry with a traceable maintainer and source. Bvostfus Python fails the first test because it isn’t in the standard library. The second test takes evidence, and the four checks below show what that evidence looks like here.
Checking PyPI and Package Metadata
The Python Package Index is where pip looks by default. On the date above, PyPI had no project named bvostfus-python, bvostfus, or bvostfus_python. PyPI treats capitalization and runs of hyphens, underscores, and dots as equivalent (PEP 503), so those three cover the obvious variants. A real listing would also show package metadata: maintainers, release dates, project links, and supported Python versions.
Checking for an Official Source Repository
A GitHub repository search for the term returned no matches on the same date. That check has limits. GitHub isn’t the only host, private repositories don’t appear in public search, and a differently spelled repository wouldn’t match. Still, legitimate open-source projects usually leave a public trail, and in the place checked, none has turned up.
Checking Documentation, Maintainers, and Release History
No maintainer-published documentation surfaced. With no registry listing, there’s no release history to read either. The site bvostfus.net describes itself as a publisher of Python tutorials and troubleshooting guides, which is different from a project’s own documentation site.
How to Distinguish a Real Project From Unverified Online Claims
Articles about software can be wrong, so read them skeptically. These are warning signs in a guide:
- No link to a registry page or source repository.
- Commands with no named source, or a vague “official source” that’s never linked.
- No version numbers, changelog, or release dates.
- Feature lists that could describe any Python tool.
- Near-identical titles and phrasing across unrelated sites.
- Confident how-to steps for software with no identified maintainer.
One or two of these can be innocent. Several together mean the guide shouldn’t be your only evidence.
Read More About : Befitnatic Website Explained: Honest Full Review, Features, Safety Check & Real User Guide
Why Are People Searching for Bvostfus Python?
Nobody outside the people using the term knows for sure. The reasons below are possibilities, not findings.
Possible Misspelling or Incorrect Package Name
Typos are the simplest explanation. But nothing points to a specific intended name, and guessing one would only add confusion. If you copied the term from a tutorial or message, recheck the spelling at the source. This matters for security too. Attackers register misspelled versions of popular package names and wait for someone to type them, a tactic called typosquatting. A package that only installs after a one-letter tweak deserves a closer look.
Private, Internal, or Unpublished Python Projects
Companies do run internal tools that never reach PyPI, often hosted on a private package index. If a coworker or employer gave you this name, ask where the documentation and index live. Nothing here shows that’s the case for Bvostfus Python. It’s simply a legitimate reason a real package can be missing from public registries.
Search Results and Repeated Online Descriptions
Search results themselves may feed the loop. Pages built around phrases like “install,” “update,” and “issue fix” attract people who then search those phrases, which encourages more pages. That’s an interpretation, not a proven cause. The pattern is visible, though: several sites publish similarly titled guides with conflicting details and no shared source.
How to Identify the Original Context Where You Encountered the Term
Where you saw the name changes what you should do next.
- A tutorial or blog post: Check its date and author, and whether it links to a registry page or repository.
- A requirements file or project code: Ask whoever wrote it. The project’s version-control history shows when the line was added.
- An error message or log: Note which command produced it, then use the troubleshooting section below.
- A colleague or employer: Ask for the package source and any internal documentation.
- An AI assistant’s answer: AI tools have been known to suggest package names that don’t exist. Check the name on PyPI before running anything.
Core Architecture of Bvostfus Python
There’s no architecture to describe. Architecture comes from source code and documentation: the modules, entry points, and ways components interact. Without a repository or published package, any description of layers or components would be invented. A guide that infers a design from what similar tools do is really describing those other tools.
If a project ever does surface, the source repository, its documentation, and the package’s file listing on PyPI are where to look. When those exist and agree, you can read the structure yourself instead of trusting someone’s summary.
Core Features of Bvostfus Python
Feature lists for the term usually mention isolated environments, automatic dependency handling, and workflow automation. Those describe what established tools such as venv, Poetry, and Conda do. They aren’t verified capabilities of Bvostfus Python. A real feature is testable: it has a documented command or setting, appears in a changelog, and works when you follow the steps in a clean environment. Anything short of that is a claim.
If you need the capabilities those lists describe, the “What Should You Use Instead?” section maps each one to a documented tool.
Read More About : MagzyMinutes.com: Your Complete Guide to Fast, Informative, and Engaging Online Content
System Requirements Before You Install
No confirmed system requirements exist for Bvostfus Python, and specific RAM or disk figures for an unverifiable package would be guesses. These four checks apply to any package.
Confirm the Correct Python Version
Run python –version, or python3 –version on macOS and Linux, or py –version on Windows. A package declares which interpreter versions it supports in its metadata, and pip checks that declaration before installing. Python releases stop receiving security fixes after a set period, so review the status of Python versions before choosing one.
Check Your Operating System and Environment
Commands differ by platform. Windows often uses python or py, macOS and Linux often use python3, and virtual environment activation paths differ too. Several Python installs can also coexist (system, Homebrew, Microsoft Store, Conda), which makes it unclear which interpreter runs your command. Processor architecture matters occasionally, because prebuilt packages aren’t available for every combination.
Confirm the Package Name and Installation Source
Before you start, know exactly what you’re installing and where it comes from: PyPI, a private index, or a Git URL. Take the exact name from the official documentation of the tool you want, not from a comment thread or a search snippet. If you can’t name a source, you aren’t ready to install.
Review Dependencies Before Running Installation Commands
Packages can pull in other packages. In recent versions of pip, adding –dry-run to an install command shows what would be installed without changing your environment. Skim that list. Unfamiliar or unexpected names are your cue to stop and investigate. Dry runs can still download files, so treat them as a preview and not a security check.
How to Install Bvostfus Python
No verified way to install Bvostfus Python exists. A few pages tell readers to run a command such as pip install bvostfus and then use a bvostfus command-line tool. On the date above, PyPI listed no such project, so those instructions have nothing to install.
The workflow below works for any package you’ve verified. It uses requests, a widely used library, purely as a stand-in. It has no connection to Bvostfus.
Check Your Python Version
Run python –version (or python3 –version) and confirm the result falls within the range the package supports. The requirements section above explains how to find that range.
Verify the Package
Stop here until the package passes the checks in the next major section.
Create a Virtual Environment
Create the environment:
python -m venv .venv
Then activate it:
- Windows (Command Prompt): .venv\Scripts\activate
- Windows (PowerShell): .venv\Scripts\Activate.ps1
- macOS and Linux: source .venv/bin/activate
Your prompt should now show the environment name. One caveat matters: a virtual environment keeps project packages separate, but it isn’t a security sandbox. Harmful code can still run and reach your files.
Install Verified Packages
python -m pip install requests
Using python -m pip ensures pip belongs to the interpreter you just activated. For a package you’ve verified, pin the version (package-name==X.Y.Z) so future installs match.
Verify Installation
python -m pip show requests
python -c “import requests; print(requests.__version__)”
pip show confirms what’s installed and where. The import test confirms Python can actually load it. If the import fails, see the ModuleNotFoundError entry below.
What to Do If No Verified Bvostfus Package Can Be Found
- Stop. Don’t try random index URLs, download links, or “official” installers from unverified pages.
- Recheck the spelling against the source where you found the name.
- Go back to that source and ask the author or your team for the package’s registry page or repository.
- If you need a capability rather than a name, choose a documented tool from the alternatives below.
- If you already ran an install command, uninstall it (python -m pip uninstall package-name), delete the virtual environment folder, and review python -m pip list for anything unfamiliar. If the command ran outside a virtual environment, or on a machine holding credentials, consider rotating those secrets as a precaution.
Nothing found so far shows the name is harmful, and nothing shows it’s safe. Unverified means you can’t tell.
Read More About : SimplifyDiggs.com Smart Digital Solutions and Insights Guide – Everything You Need to Know
How to Verify an Unknown Python Package Before Installing It
Installing a package runs someone else’s code on your computer, so a few minutes of checking is cheap insurance. Typosquatting (a fake package with a near-identical name) and dependency confusion (a public package overriding an internal one) are known software supply-chain attack methods. No single check proves a package is trustworthy. The goal is a rule you can apply quickly: if you can’t find a maintainer, a source repository, and documentation that agree with each other, don’t install it.
Check the Exact Package Name
Compare the name to the one in the tool’s official documentation, letter by letter. PyPI treats hyphens, underscores, dots, and capitalization as equivalent, so my_pkg and My-Pkg point to the same project. Lookalikes with swapped, doubled, or missing letters don’t. Copy names from official docs, not from comments or search snippets.
Inspect the PyPI Listing
On the project’s PyPI page, look at who maintains it, when versions were uploaded, and where the project links lead. A trustworthy listing links to a real repository, and that repository links back. That chain is the package’s provenance, and PyPI marks some project links as verified. A description that reads like a copied README or promises vague benefits is a weak sign. Download counts and star ratings help less than you’d expect, because they can be inflated.
Check the Source Repository and Maintainer
Open the repository and ask whether the code matches the package’s name and purpose. Look for commit history spread over time, not one bulk upload. Check the maintainer’s profile and other projects. Recent activity, answered issues, and tagged releases that match the PyPI versions are healthier signs than a single commit and an empty README.
Review Dependencies and Release History
Scan the dependency list for names you don’t recognize or that don’t fit the package’s purpose. Then read the release history. Patterns worth a second look include a burst of releases in one day, large version jumps, a long silence followed by sudden changes, and an abrupt switch of maintainer. None of these proves anything bad. They’re reasons to look closer.
Check Documentation, License, and Issue History
Real projects explain what they do. Without documentation you can’t evaluate behavior, so you can’t evaluate risk. Look for a license, usage examples that match the actual code, and an issue tracker with genuine user reports. A published security policy is a plus. To see whether a project is still maintained, check for recent commits and replies from the maintainers.
Avoid Untrusted Installation Commands and Package Sources
Don’t run commands or install from URLs you can’t trace to the project’s own documentation. Two details matter. Installing from a source distribution can execute build code on your machine, and any installed package runs code when you import it. Also, pip’s –extra-index-url option makes pip consider several indexes and pick the best version it finds, which is the mechanism behind dependency confusion. Use it only with indexes you control.
Common Issues and How to Fix Them
Most install failures trace back to a handful of causes. Each entry below runs from symptom to cause to fix. The last one helps you tell an environment problem from a package that doesn’t exist.
ModuleNotFoundError
ModuleNotFoundError: No module named ‘x’ means the interpreter that’s running can’t find that module. Common causes: the package isn’t installed there, you’re using a different interpreter than the one you installed into (see the pip mismatch entry below), or the import name differs from the install name. You install pillow but import PIL, and you install scikit-learn but import sklearn.
A file in your project named like a module can also shadow it. Check with python -m pip list and python -c “import sys; print(sys.executable)”. For a module called bvostfus, the error simply means nothing by that name is installed, which is expected if no package exists.
Dependency Conflicts
Two packages sometimes need incompatible versions of a third. pip reports this as a resolver error, such as “Cannot install X and Y because these package versions have conflicting dependencies,” or warns that its dependency resolver doesn’t account for everything installed. Try a fresh virtual environment, read which versions clash, and adjust the constraints. python -m pip check lists broken requirements in an existing environment. Installing related packages in one command often gives the resolver a better chance than adding them one at a time.
Environment Not Activating
On macOS and Linux, forgetting source is the usual culprit, because running the script directly won’t change your shell. On Windows, use the Scripts folder, not bin. In PowerShell, you may see an error saying running scripts is disabled. The Python documentation suggests allowing local scripts for your user with Set-ExecutionPolicy -ExecutionPolicy RemoteSigned -Scope CurrentUser. Alternatively, use Command Prompt and .venv\Scripts\activate.bat. If a broken environment still won’t activate, deleting the folder and recreating it is faster than debugging it.
Version Mismatch Errors
An error like Package ‘x’ requires a different Python: 3.9.7 not in ‘>=3.11’ means the package doesn’t support your interpreter. Check your version, then install a supported Python or choose a different release of the package. Tools like pyenv and uv can manage several Python versions side by side. Avoid pip’s –ignore-requires-python flag. It bypasses a safeguard and often produces confusing failures later.
Package Not Found or No Matching Distribution
ERROR: Could not find a version that satisfies the requirement x (from versions: none), followed by ERROR: No matching distribution found for x, means pip found nothing installable under that name on the index it searched. Causes include a name that doesn’t exist, a typo, no build for your Python version or platform, an outdated pip, and network, proxy, or index configuration problems. Check the name on PyPI first, then run python -m pip –version and update pip if it’s old. Don’t “fix” the error by adding unfamiliar index URLs or downloading files from a page you can’t trace. That’s exactly how people end up installing something malicious.
Incorrect Package Name or Typo
Sometimes an error vanishes after you change a single letter, and that’s the moment to pause. You may have just installed a different package, possibly one built to catch typos. Run python -m pip show name and check that project’s PyPI page. Confirm it’s what you meant, and uninstall it if it isn’t.
pip and Python Environment Mismatch
When pip and python belong to different installations, packages land where your code can’t see them. Run python -m pip –version and pip –version, then compare the paths. Using python -m pip for every install keeps the two aligned. On some recent Linux distributions, pip refuses to modify the system Python and shows an “externally-managed-environment” error (PEP 668). The fix is a virtual environment, not overriding the protection.
When an Error Indicates That the Package Itself Cannot Be Verified
Not every failure is your environment’s fault. This table helps separate the two.
| What you see | Usually points to | Next step |
| “No matching distribution found” for this package only, while others install fine | A name that doesn’t exist on the index, or a typo | Check the name on PyPI and at the original source |
| ModuleNotFoundError right after a successful install | Wrong interpreter or import name | Check sys.executable and the import name |
| “Requires a different Python” | Version mismatch | Use a supported interpreter |
| “Conflicting dependencies” | Clashing version constraints | Fresh environment, adjust constraints |
| A guide’s command works only after adding another index or download link | An untraceable source | Stop and verify before continuing |
If the same package fails everywhere and no registry page exists, treat “not found” as information rather than an obstacle.
Read More About : Thesindi com Explained: Simple Guide to Features & Use Online
How to Update Bvostfus Python
No official update path exists, because no verified release exists to update. Upgrade commands on other sites have no documented source. The steps below apply to any package you’ve verified.
Check Whether an Official Release Exists
Read the project’s release history on its PyPI page and any changelog in its repository. Compare against your installed version with python -m pip list –outdated. For Bvostfus Python there’s no release history to consult, so there’s nothing to compare against.
Verify the Package Source Before Updating
Updates aren’t automatically safe. Maintainers change, accounts get compromised, and a project you trusted last year can ship something different today. Before upgrading, confirm the package still comes from the same source and maintainer, and that the release notes match what actually changed.
Review Version and Dependency Changes
Read the changelog first. Then upgrade in a throwaway environment and compare python -m pip freeze before and after, which shows every package that changed, including indirect ones. Run your tests before touching your main environment.
What to Do When No Reliable Update Path Exists
Keep what you have pinned to its current version, and don’t update from an untraceable source. If it’s an internal tool, ask its maintainers for the supported update process. If nobody can answer, plan a replacement. Software you can’t update or verify becomes a liability over time.
Package Compatibility and Integration
Nothing supports claims that Bvostfus Python works with Django, NumPy, TensorFlow, or any other library, so don’t rely on lists that say so. You can, however, judge compatibility for any package yourself.
Python Version Compatibility
Look for two kinds of evidence. Declared support is what the package’s metadata says. Tested support is what the project’s automated tests actually run against, which usually appears in the repository’s continuous integration configuration. Declared-only support is a promise, while tested support is a track record. A compatibility matrix in the documentation helps when one exists.
Dependency Compatibility
Read the version constraints a package places on its dependencies before adopting it. Tight pins (==) leave little room for other packages, and very wide ranges can let breaking changes slip in. pip’s resolver looks for a set of versions that satisfies every constraint and reports a failure when none exists.
Virtual Environments and Isolated Projects
Give each project its own environment, and try unfamiliar packages in a disposable one you can delete afterward. That keeps a bad experiment from tangling with your working setup.
Integration With Existing Python Projects
Adding a dependency changes your project. Ask which code will import it, what happens if it disappears, and how you’d roll back. Record it in your dependency file with a pinned version, and make the change on a branch in version control so you can revert cleanly. Run your test suite before merging.
How to Verify Compatibility Before Adding an Unknown Dependency
- Do you actually need it, or does a tool you already use cover the task?
- Is it maintained, with recent releases and answered issues?
- Does it install in a clean environment?
- Do your tests pass with it added?
- Could you remove it easily?
If any answer is no, pause before it reaches production.
Read More About : Latest News My Green Bucks.net – Don’t Miss These New Updates!
Real-World Applications
No verified real-world use of Bvostfus Python exists. Python itself powers web apps, data work, and automation, but those strengths belong to Python and its established libraries, not to a name that can’t be traced to any software.
To judge whether any tool is genuinely used, look for named organizations that say so, public repositories that depend on it, and an active issue tracker where real users report real problems. Statements like “developers use it to speed up workflows,” with no names attached, are marketing copy.
Performance Benefits You Actually Notice
There’s no performance data for Bvostfus Python, so there’s nothing to notice. Some pages claim faster workflows or fewer errors, but none offers a benchmark, a method, or a measurable result.
A credible performance claim states the hardware, Python version, package versions, and test method, and it gives numbers someone else can reproduce. If a page can’t show that, treat the benefit as unproven. Some improvements people credit to a tool actually come from habits like isolated environments and pinned dependencies, which work with any tool.
Tips for Beginners
A few habits prevent most of the trouble covered above.
Start With a Virtual Environment
Create one environment per project, give it a consistent name like .venv, and keep it out of version control. Avoid installing project packages into your system Python. That’s how conflicts and “externally managed” errors begin.
Verify Unfamiliar Packages Before Installation
Ask three questions before any install command. Is there a PyPI page for this exact name? Does it link to a real repository? Do you know why you need it? A “no” to any of them means slow down.
Keep Dependencies Documented
List what your project needs in a requirements.txt or pyproject.toml so anyone, including future you, can rebuild the environment. python -m pip freeze records everything installed, including indirect dependencies. That’s handy for a snapshot but noisy for a hand-maintained list.
Read Errors Before Changing Multiple Settings
Start with the last line of the traceback, because it names the actual error. Change one thing at a time so you know what fixed it, and search the exact message rather than a paraphrase. When you ask for help, include the full error and the commands you ran.
Use Official Documentation Whenever Available
The Python documentation, the Python Packaging User Guide, and the pip documentation cover virtual environments, installing packages, and error messages, and they stay current. Prefer them over tutorials with no date or author.
Advanced Usage Techniques
Once the basics feel routine, you can add stronger controls for dependencies you can’t fully vouch for. None of these makes an unknown package safe, but each narrows the risk.
- Hash-checking mode. pip’s –require-hashes installs only files whose hashes match the ones you recorded, so a swapped file fails.
- Lock files. Tools like pip-tools, Poetry, and uv can record exact versions of every dependency for repeatable installs.
- Known-vulnerability scans. pip-audit checks installed packages against databases of known vulnerabilities. It won’t catch malware nobody has reported.
- Disposable test environments. Try an unfamiliar package in a container or virtual machine with no access to your credentials or important files.
- Reading before building. Inspect a source distribution’s contents before installing it, since building it can run code.
- Private mirrors. Teams can restrict installs to an index they control.
Read More About : TechInsiderz.com Gadgets: Expert Reviews, News & Top Picks 2026
Bvostfus Python vs Traditional Python Setup
This isn’t a comparison between two equal options. It sets a documented workflow next to a name nobody can document.
What a Standard Python Setup Provides
A standard setup gives you the interpreter from python.org, the standard library, venv for isolated environments, pip for installing packages, and PyPI as the main public index. Each has official documentation, a public issue process, and a large community. That’s the baseline to measure any newcomer against.
What Can Actually Be Verified About Bvostfus Python
| Criterion | Standard Python setup | Bvostfus Python (as of Sept. 28, 2026) |
| Official documentation | Yes, at python.org and in pip’s docs | None found from a maintainer |
| Registry listing | pip installs from PyPI | No PyPI project found under the names tried |
| Public source repository | CPython and pip are open source | None found in a GitHub search |
| Release history | Public and versioned | None to review |
| Named maintainers | Python Software Foundation; PyPA for pip | None identified |
| Support channels | Docs, forums, issue trackers | Only third-party guides |
| Update process | Documented | None documented |
Each empty cell is a question worth answering before you trust the name.
Differences in Installation and Dependency Management
With a standard setup, the workflow is documented end to end: create an environment, install from a named source, record dependencies in a file, and upgrade deliberately. For Bvostfus Python, no verifiable version of that workflow exists. The only “process” comes from third-party pages that can’t point to the software itself.
When a Standard Python Workflow May Be More Appropriate
Almost always. The exception is a team that gives you internal, verifiable documentation for a private package. In that case, follow those docs and confirm the source with the people who maintain it. For everything else, a documented tool that fits your goal beats an unverifiable one.
What Should You Use Instead?
Since nobody can say what Bvostfus Python does, the right replacement depends on what you were trying to do.
Established Python Package and Environment Tools
A handful of tools cover most of what people describe wanting. venv ships with Python and creates isolated environments, and virtualenv does similar work with more options. pip installs packages. Poetry manages dependencies and packaging with a lock file. Conda handles packages and environments, including non-Python software, and is popular in data science. pipx installs Python command-line apps in isolated environments. uv is a newer, fast tool for environments and packages, and pyenv manages multiple Python versions.
Choosing a Replacement Based on Your Actual Development Need
| If you need to… | Look at |
| Keep one project’s packages separate from another’s | venv or virtualenv |
| Install packages from PyPI | pip |
| Lock exact dependency versions and manage packaging | Poetry, or lock files from pip-tools or uv |
| Manage non-Python dependencies, such as data science stacks | Conda |
| Install command-line Python apps without cluttering environments | pipx |
| Run several Python versions | pyenv or uv |
| Speed up environment and package operations | uv |
How to Verify an Alternative Before Installing It
Even well-known tools deserve the same care. Install them from their official documentation, confirm the exact package name, and apply the checks from the verification section above. Popular names attract lookalikes.
Frequently Asked Questions
Is bvostfus python an official Python project?
No. It isn’t part of Python or its standard library, and no verified third-party project by that name has turned up. As of September 28, 2026, neither PyPI nor a GitHub search found one.
Can I install bvostfus python?
No verified installation package or documentation exists. Skip install commands from pages that can’t point to a maintainer and a source repository. If a project by that name ever appears, verify who published it first.
Why are people searching for bvostfus python?
Possible reasons include typos, internal company tools, and repeated online descriptions that generate more searches. None is confirmed.
Is it safe to install unknown Python packages?
Not by default. Installing can run code, and a virtual environment doesn’t sandbox it. Check the name, PyPI listing, repository, and maintainer first.
What should I use instead?
It depends on your goal. Use venv or virtualenv for isolated environments, Poetry or uv for dependency locking, and Conda for data science stacks. The table above matches each need to a tool.
Is Bvostfus Python available on PyPI?
Not as of September 28, 2026. PyPI had no project named bvostfus-python, bvostfus, or bvostfus_python. Names can be registered at any time, so check the listing yourself before installing anything.
Does Bvostfus Python have an official GitHub repository?
None turned up in a GitHub repository search on the same date. Public search doesn’t cover private repositories or other hosting sites, but no repository has been identified.
Why does pip install bvostfus fail?
A “No matching distribution found” error means pip couldn’t find a project by that name on the index it searched, which fits the PyPI results above. Check the spelling, your pip version, and your network or index settings. Don’t work around it with unfamiliar download links. And if the command ever succeeds, look up who published the package before trusting it.
Is Bvostfus Python a framework or library?
Neither has been verified. Sites use labels ranging from framework to package to learning approach, with no source behind any of them.
Could Bvostfus be a misspelled package name?
It could, but there’s no evidence of a specific intended name. Recheck the spelling wherever you found it, and avoid guessing at similar package names.
How can I verify an unfamiliar Python package?
Check the exact name, read its PyPI page, and follow the project links to a real source repository. Then look at maintainers, release history, dependencies, documentation, and license. Consistent evidence across those checks is what builds trust.
Final Thoughts
As far as the available evidence shows, Bvostfus Python is a name without software behind it. The useful takeaway is the habit it teaches. Before you run a pip command, know the exact package name, the registry page, the source repository, and the maintainer.
Things can change. If a maintainer, repository, and documentation ever appear and agree with each other, the same checks will tell you whether to trust them. Until then, pick a documented tool for the job you actually need to do.